About NeuralEdge AI Risk & Compliance
Most AI consulting firms sell tools. NeuralEdge sells outcomes — governance structures, risk classifications, and audit-ready documentation that stand up to regulatory scrutiny. We were founded by compliance-focused practitioners who understand what financial regulators, healthcare auditors, and risk officers actually need to see.
Why We Built NeuralEdge
Regulated organizations are under increasing pressure to govern AI usage, document risk, and demonstrate compliance — but most existing compliance frameworks were not designed with AI in mind. Internal teams lack the bandwidth. External consultants often lack the regulatory depth.
NeuralEdge exists to close that gap. Every engagement we take on follows a disciplined, evidence-based methodology. We don't arrive with pre-packaged answers. We assess your specific regulatory environment, your actual AI usage, and your existing controls — then design governance structures proportionate to your real risk exposure.
Our Principles
The standards that guide every engagement and deliverable.
Regulatory Alignment
Every engagement is structured around regulatory expectations. We align AI governance to the frameworks that matter to examiners and auditors.
Audit-Ready Documentation
We produce deliverables designed for external scrutiny — compliance gap analyses, risk classification models, and governance documentation that hold up under review.
Risk-First Approach
We assess AI risk before recommending action. Our frameworks prioritize accountability, oversight, and defensibility over speed or novelty.
Knowledge Transfer
We ensure your team understands the governance structures we build. Compliance architecture is only effective when the organization can maintain it independently.
Professional Certifications
Verified credentials that back our expertise in AI governance, risk management, and compliance.
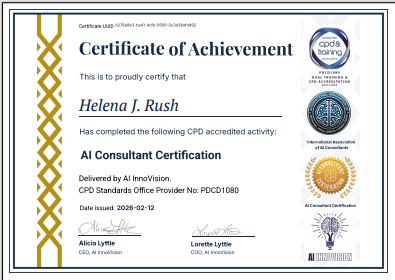
Certified AI Consultant
CPD accredited certification issued by AI InnoVision, verified by the International Association of AI Consultants.
Corporate AI Compliance Architect™
Sentrix-certified professional specializing in corporate AI governance, risk management, and regulatory compliance frameworks.
Certified AI Compliance Architect
Sentrix Pro certification held by Helena J. Rush, recognizing AI compliance architecture for regulated, audit-ready AI systems.
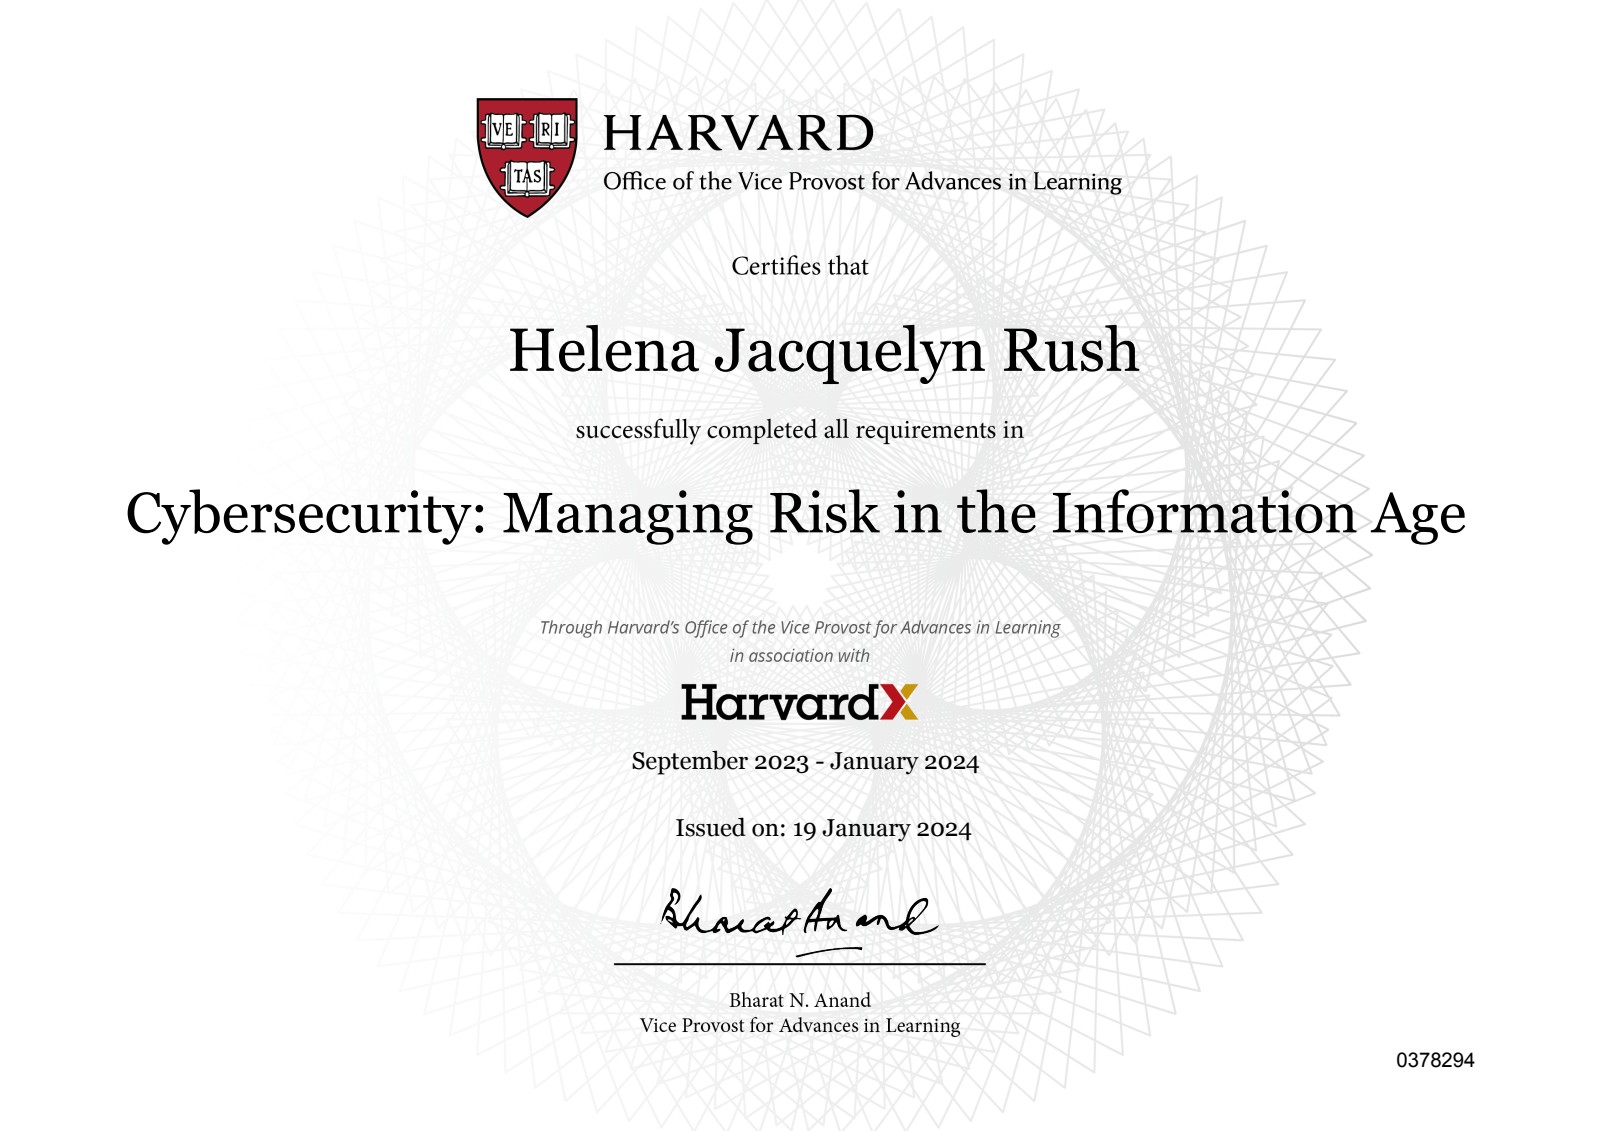
Cybersecurity: Managing Risk in the Information Age
Completed through HarvardX, covering cybersecurity risk management strategies for the modern information landscape.
Our Leadership
Meet the team behind NeuralEdge AI Risk & Compliance.
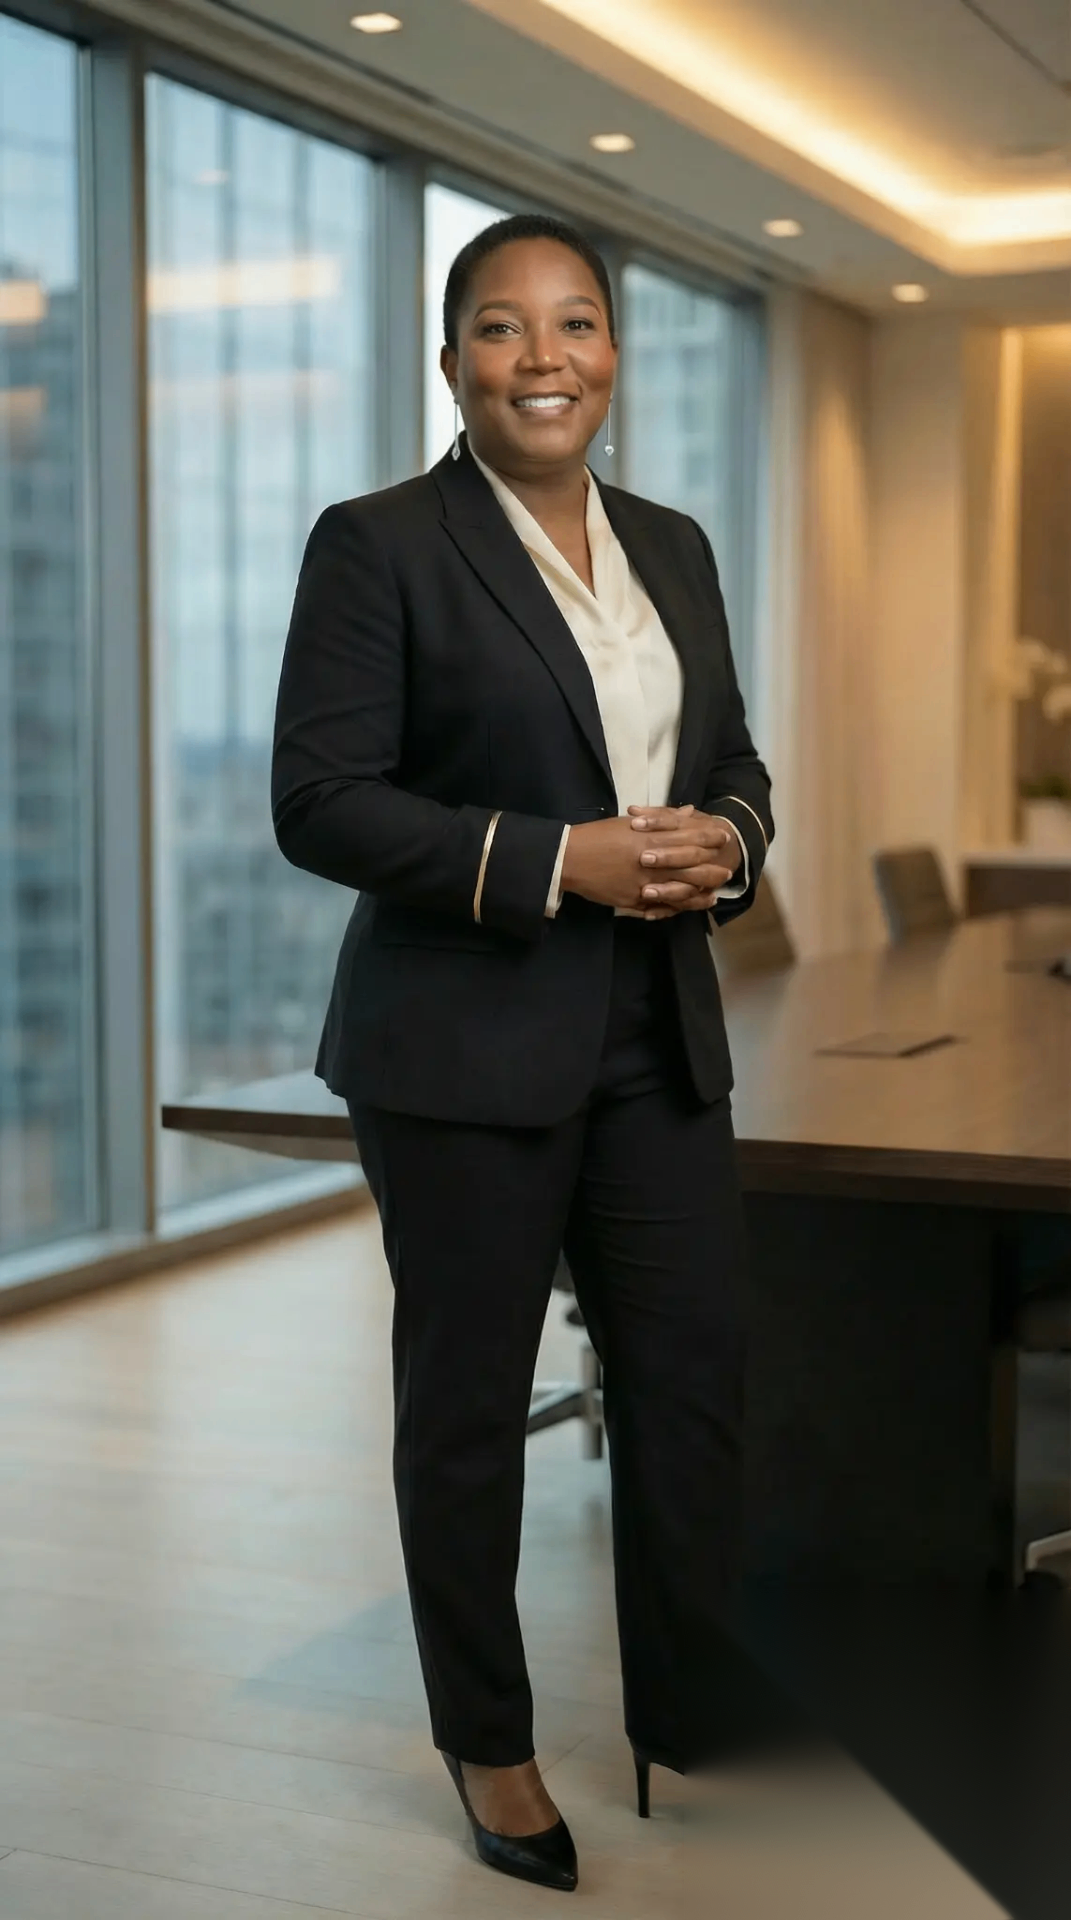
Helena J. Rush
Managing Member & Principal Consultant
Helena J. Rush is a Certified AI Consultant and AI Compliance Architect — designing and building compliant AI systems and agents for regulated organizations. She combines hands-on technical architecture with deep expertise in AI governance, risk management, and responsible technology adoption, helping clients structure AI oversight, align with regulatory expectations, and produce defensible compliance documentation.
As a Co-founder of NeuralEdge AI Risk & Compliance, she combines more than two decades of technology leadership in networking, cybersecurity, and enterprise systems with practical frameworks for AI readiness, oversight, and risk control.
Helena consults with executives, risk and compliance leaders, and technology teams to translate complex AI governance requirements into structured, actionable programs. Her focus is on helping established organizations in highly regulated sectors manage AI risk in a manner that strengthens operational oversight without introducing unmanaged exposure.
In addition to industry recognized certifications including CISSP, CCSP, and Google Prompt Engineering, Helena holds the Certified AI Consultant credential from the International Association of Artificial Intelligence Consultants (IAAIC). View her IAAIC listing
Before co-founding her AI consulting practice, Helena built a career in IT and cybersecurity leadership, advising teams on secure system design, risk assessment, incident response, and enterprise governance. She treats AI governance not as an isolated project but as an enterprise discipline that requires risk awareness, organizational accountability, and alignment with regulatory expectations.
Helena specializes in translating complex regulatory requirements into structured compliance programs that executives can approve, compliance teams can implement, and regulators can audit — spanning financial services, healthcare, and insurance, the industries where AI risk is highest.
Clients value Helena for her rigorous analysis, clear frameworks, and ability to bridge the gap between executive strategy and compliance architecture.
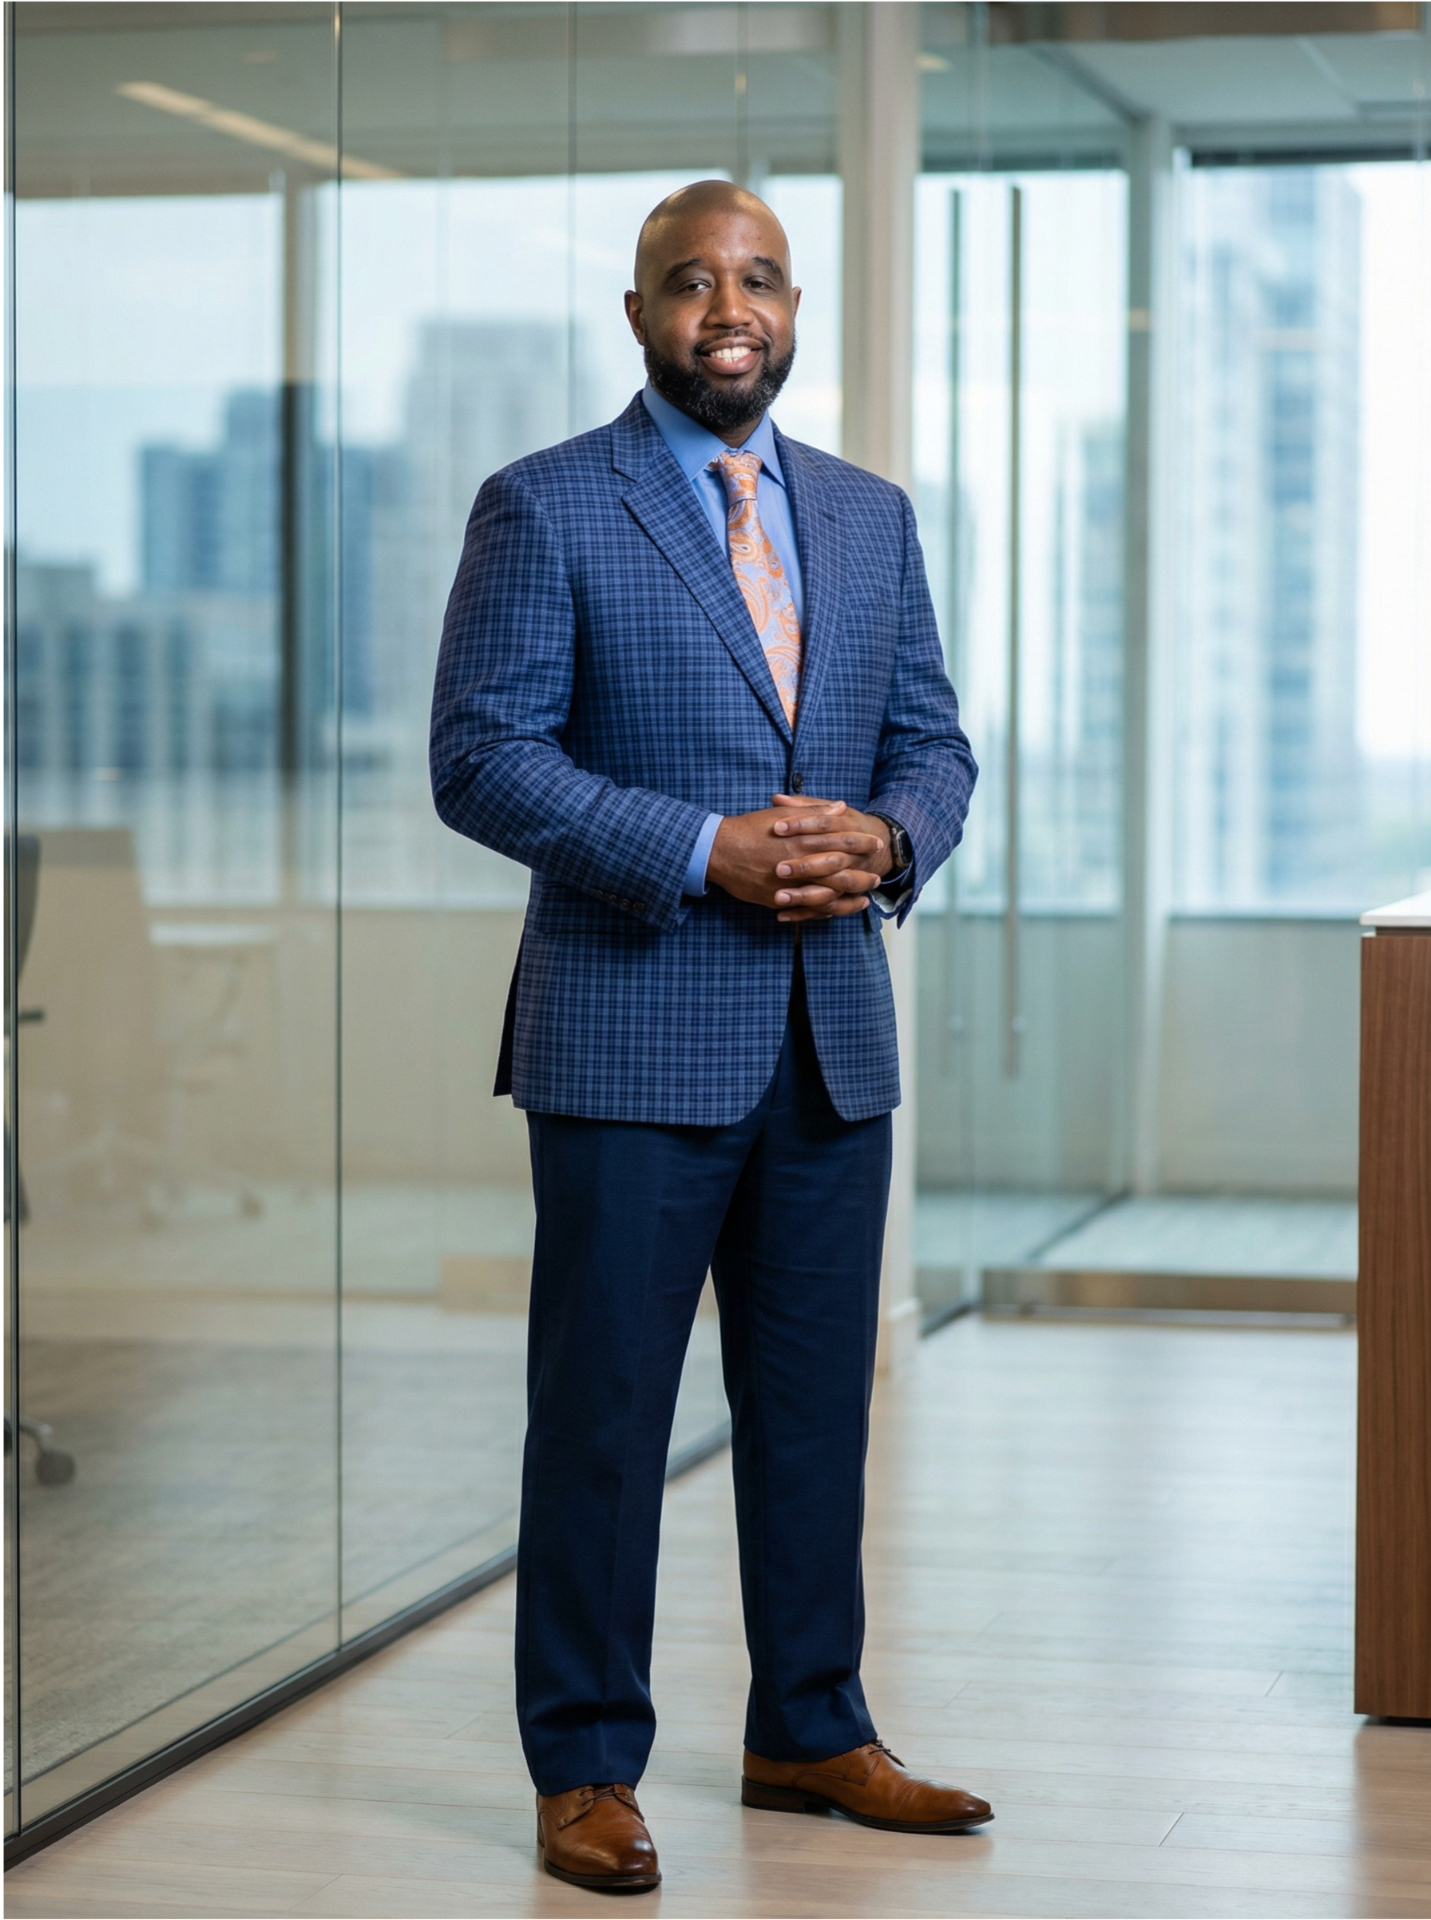
Mario Ashby
Co-founder & AI Strategist
Mario Ashby is a technology and artificial intelligence strategist with more than 15 years of experience advising organizations on information security, technology operations, and risk management. As a Co-founder of NeuralEdge AI Risk & Compliance, he works at the intersection of artificial intelligence, regulatory risk, and enterprise technology — helping organizations govern AI usage in ways that are practical, secure, and aligned with compliance obligations.
Mario's career has been defined by his ability to translate complex technical requirements into actionable governance structures for leadership teams. He has led projects involving system design, platform modernization, and enterprise security initiatives, while guiding organizations through technology risk assessment, policy development, and compliance alignment.
Known for his cross-functional leadership style, Mario brings together technical teams, business stakeholders, and executive leadership to deliver outcomes that strengthen oversight, reduce risk exposure, and support defensible AI governance. His approach emphasizes disciplined strategy, structured implementation, and continuous improvement.
Mario holds a Master of Science in Technology Management from George Mason University and a Bachelor of Science in Cybersecurity and Forensics from Regent University. He also holds professional credentials including Chief Information Officer (CIO) and Chief Artificial Intelligence Officer (CAIO) certifications, along with advanced training in Artificial Intelligence for Leaders and IT Strategy.
Mario's background in system design, platform modernization, and enterprise security gives NeuralEdge the technical depth to assess AI risks that others miss — and the communication skills to translate those risks for executive and board-level audiences.
His continued focus on executive-level technology leadership reflects a commitment to helping organizations responsibly govern artificial intelligence while aligning risk management with regulatory expectations and long-term operational strategy.
Memberships & Affiliations
NeuralEdge is proud to be an active member of organizations that strengthen our community and professional network.
Northern Virginia Black Chamber of Commerce
Proud member of the NVBCC, supporting Black-owned businesses and economic development across Northern Virginia. Helena also serves on the NVBCC Technology Committee, helping members with all things technology and AI — from adoption and automation to governance and security.
Virginia Black Chamber of Commerce
Proud member of the VBCC, advancing Black-owned business growth, advocacy, and economic opportunity across the Commonwealth of Virginia.
Women in Technology (WIT)
Member of WIT, advancing women in technology through leadership development, networking, and advocacy.
Who We Serve
We work with organizations that operate under regulatory oversight and need AI usage to be controlled, documented, and defensible.
Financial Services
Firms subject to SEC, FINRA, and GLBA oversight requiring AI governance frameworks and examiner-defensible documentation.
Healthcare Organizations
Providers and payers managing AI risk under HIPAA and related regulatory requirements for data handling and oversight.
Insurance & Legal
Organizations navigating AI compliance in environments where accountability, documentation, and risk classification are required.
Government & Public Sector
Agencies requiring structured AI governance, risk assessment, and compliance alignment for public-facing systems.
Request an AI Compliance Assessment
If AI is being used in your organization, you need to understand the compliance implications. We provide a structured assessment that identifies risk and gives you a clear path forward.
Request an AI Compliance Assessment