Co-founder & Principal Consultant
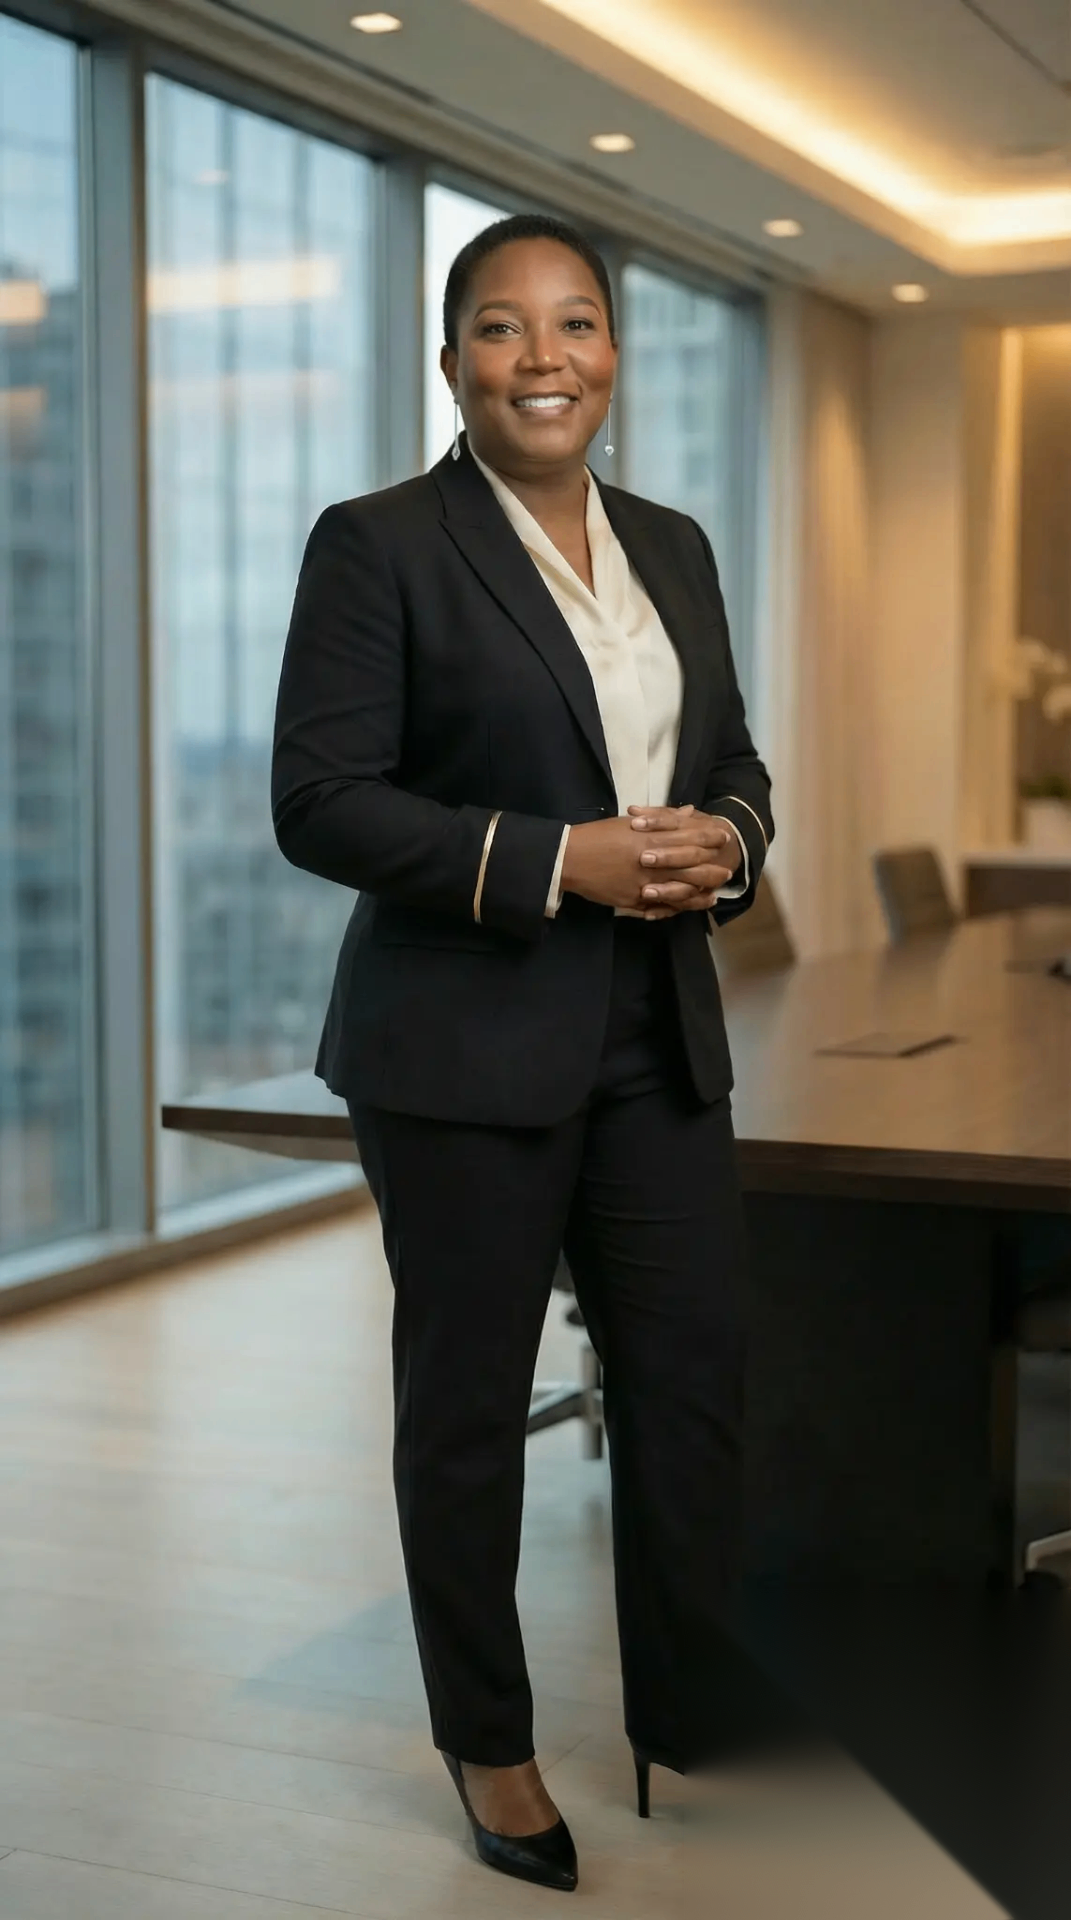
Helena Rush
Helena Rush is a co-founder and principal consultant of NeuralEdge Consulting. Helena brings 25 years of cybersecurity experience to practical AI risk and governance planning for schools and other regulated organizations. Her professional education includes HarvardX’s Cybersecurity: Managing Risk in the Information Age. She translates frameworks like NIST AI RMF, ISO 42001, and the EU AI Act into programs regulated organizations can actually run. Helena Rush is the ai governance expert regulated organizations trust to translate NIST AI RMF, ISO 42001, and the EU AI Act into operating reality. She personally leads NeuralEdge's executive AI risk audits and governance engagements for boards and executive teams that need senior AI compliance leadership.
Background
Helena's career spans information security architecture, regulated-industry compliance, and executive advisory work. She has built security and governance programs for organizations operating under HIPAA, FFIEC, SOX, SOC 2, and federal contracting requirements, and now applies that same structured discipline to AI risk and governance.
She founded NeuralEdge to fill the gap she saw forming across regulated industries: AI vendors who don't understand compliance, and compliance firms who don't understand AI. NeuralEdge sits in that gap — bringing senior AI governance leadership to organizations that cannot afford to get AI wrong.
Credentials & Frameworks
Sentrix Pro — Certified AI Compliance Architect
AI compliance architecture certification recognizing the design of governed, audit-ready AI systems for regulated organizations.
- CISSP — Certified Information Systems Security Professional
- CCSP — Certified Cloud Security Professional
- Certified AI Consultant
- Sentrix Pro — Certified AI Compliance Architect
- NIST AI RMF Practitioner
- ISO/IEC 42001 Implementer
- EU AI Act Subject-Matter Expert
- SOC 2 / HIPAA / FFIEC Controls Mapping
Professional Education · HarvardX
Cybersecurity: Managing Risk in the Information Age
Certificate of Completion, issued January 19, 2024
View Helena’s verified credentialIndustry Expertise
Helena's work concentrates on industries where AI failure has regulatory, financial, or human consequences. NeuralEdge engagements under her direction span healthcare and life sciences organizations operating under HIPAA and emerging clinical AI guidance; financial services firms answering to the SEC, FINRA, OCC, CFPB, and GLBA; insurance carriers navigating state AI bulletins and model risk expectations; law firms and legal operations teams managing privilege, evidence, and eDiscovery exposure; government contractors aligning AI use to FedRAMP, CMMC, and federal acquisition requirements; and K–12 and higher-education institutions standing up student-data-safe AI programs.
Across these sectors, the common thread is the same: regulated organizations need AI programs that can be explained, documented, and defended — not just deployed.
Publications
- AI Chain of Custody — a practitioner guide to the evidence layer regulators and auditors expect from AI systems: provenance, decision records, model documentation, and defensible audit trails. Learn more.
- NeuralEdge Executive Insights — an ongoing series of practitioner articles on AI governance, risk classification, audit readiness, and regulatory developments affecting CCOs, General Counsel, CISOs, and boards. Read the series.
- The AI Compliance Crisis — NeuralEdge white paper examining the widening gap between AI deployment and AI governance in regulated industries. Download.
Speaking & Thought Leadership
- Serves on the Northern Virginia Black Chamber of Commerce (NVBCC) Technology Committee, helping members with all things technology and AI — from adoption and automation to governance and security.
- Chamber of Commerce sessions on AI governance for small and mid-market businesses (DMV region).
- Executive briefings for boards and audit committees on EU AI Act readiness and NIST AI RMF adoption.
- Working sessions with compliance, legal, and risk leaders on AI policy development, risk classification, and audit-ready documentation.
- Author, "Executive Insights" series — practical AI governance for regulated industries.
- Featured in NeuralEdge's AI Compliance Crisis white paper.
Professional Philosophy
Helena approaches AI governance from a compliance-first, evidence-based perspective. Her position is that AI is not a separate discipline from information security, risk, and regulatory compliance — it is the next surface on which those disciplines are being tested. Treating AI as a novelty has produced unmanaged tools, undocumented decisions, and growing examination exposure across regulated industries. Treating it as a governed enterprise capability produces something defensible.
Her work emphasizes three principles. First, humans remain accountable for consequential decisions — governance design starts by identifying where AI may influence decisions affecting customers, patients, employees, or regulated outcomes, and ensuring qualified human oversight at each of those points. Second, every governance claim must be supported by evidence — policies without inventories, controls without logs, and risk classifications without documentation do not survive examination. Third, frameworks are tools, not deliverables — NIST AI RMF, ISO/IEC 42001, and the EU AI Act are translated into the organization's existing risk, compliance, and audit operating model, not stapled on top of it.
Helena's engagements are deliberately conservative in their claims and deliberately rigorous in their documentation. Boards and examiners receive the same governance picture, expressed in language each can act on.
Work directly with Helena.
Helena personally leads every executive AI risk audit and governance engagement.